
Frameworks
Work multiple frameworks without repeating the work
Frameworks overlap. CyberComply lets you organize requirements across them in one environment, so evidence and assessment work can be reused where the mapping is valid.
Inside the product
One framework library, one environment
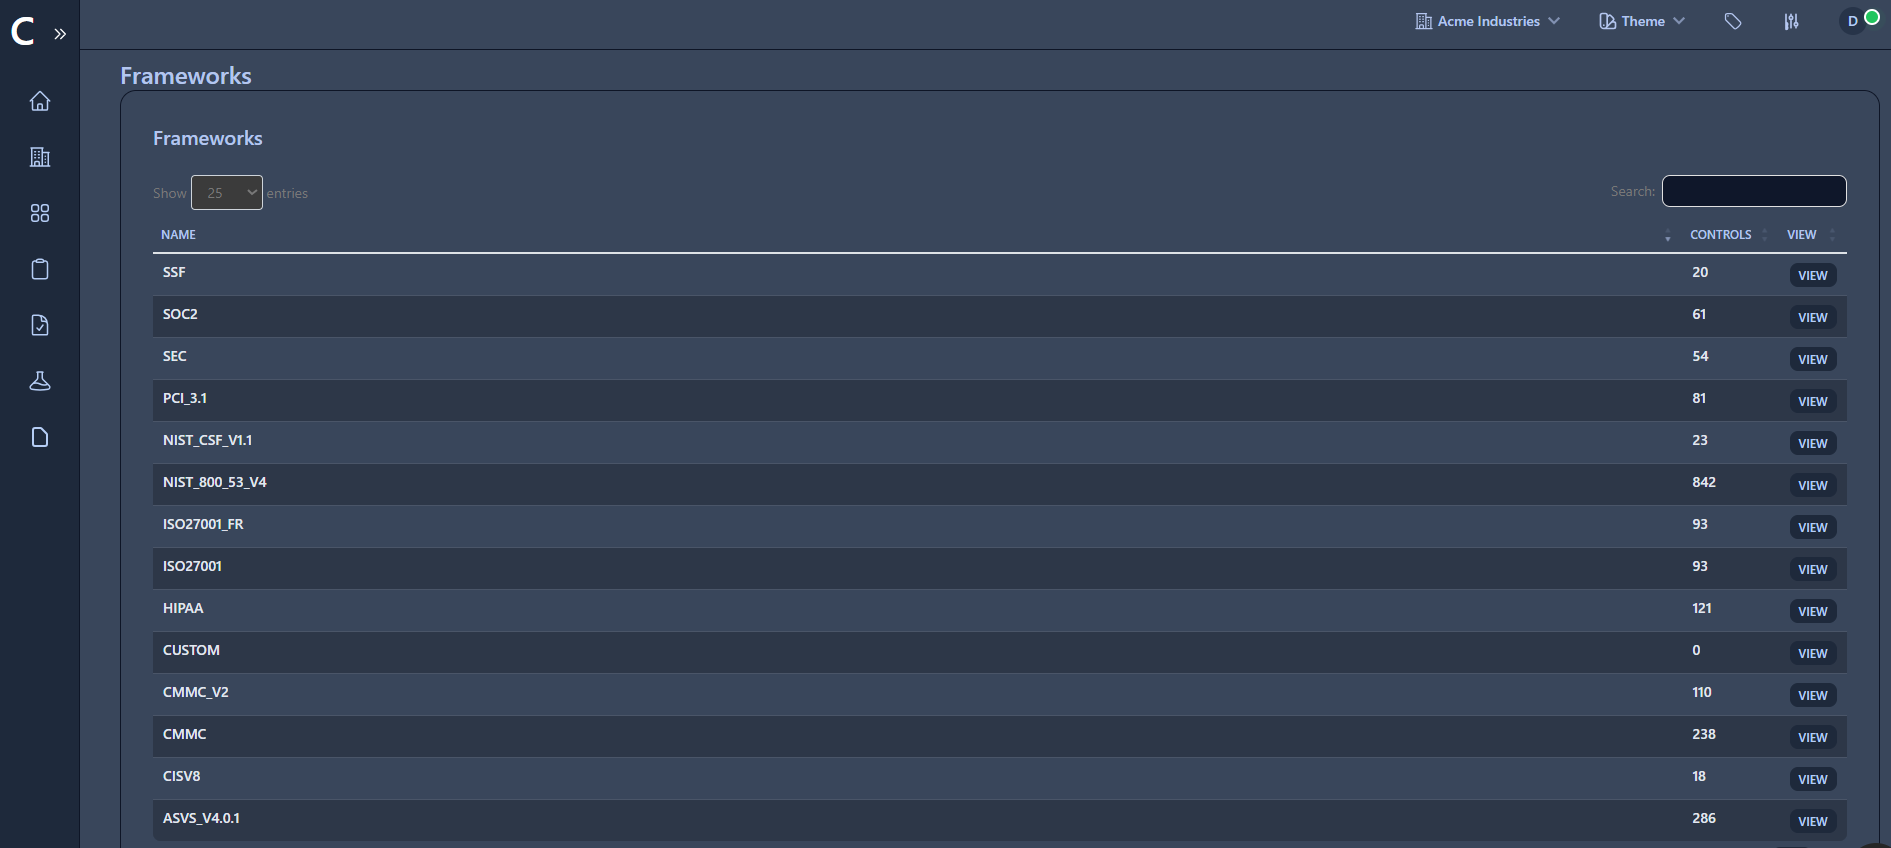
Frameworks are managed side by side in CyberComply, each with its own control set, so work stays organized per framework while living in the same program.
Federal & Defense
Federal & Defense frameworks
CMMC
DoD contractors handling FCI and CUI.
CMMC details →NIST SP 800-171
Protecting CUI in nonfederal systems.
NIST 800-171 details →NIST Cybersecurity Framework
Organizing cybersecurity risk outcomes.
NIST CSF details →NIST SP 800-53
Security and privacy controls for information systems.
NIST 800-53 details →Commercial & Regulatory
Commercial & Regulatory frameworks
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.