
Capability
Scope is a decision. Record it.
Maintain the systems, environments, and asset records that define the boundary your compliance program applies to.
Scoping errors are expensive. A boundary that exists only in one person's head cannot be reviewed, challenged, or defended.
CyberComply keeps asset and system records alongside the requirements that apply to them, so the scope of the program is explicit.
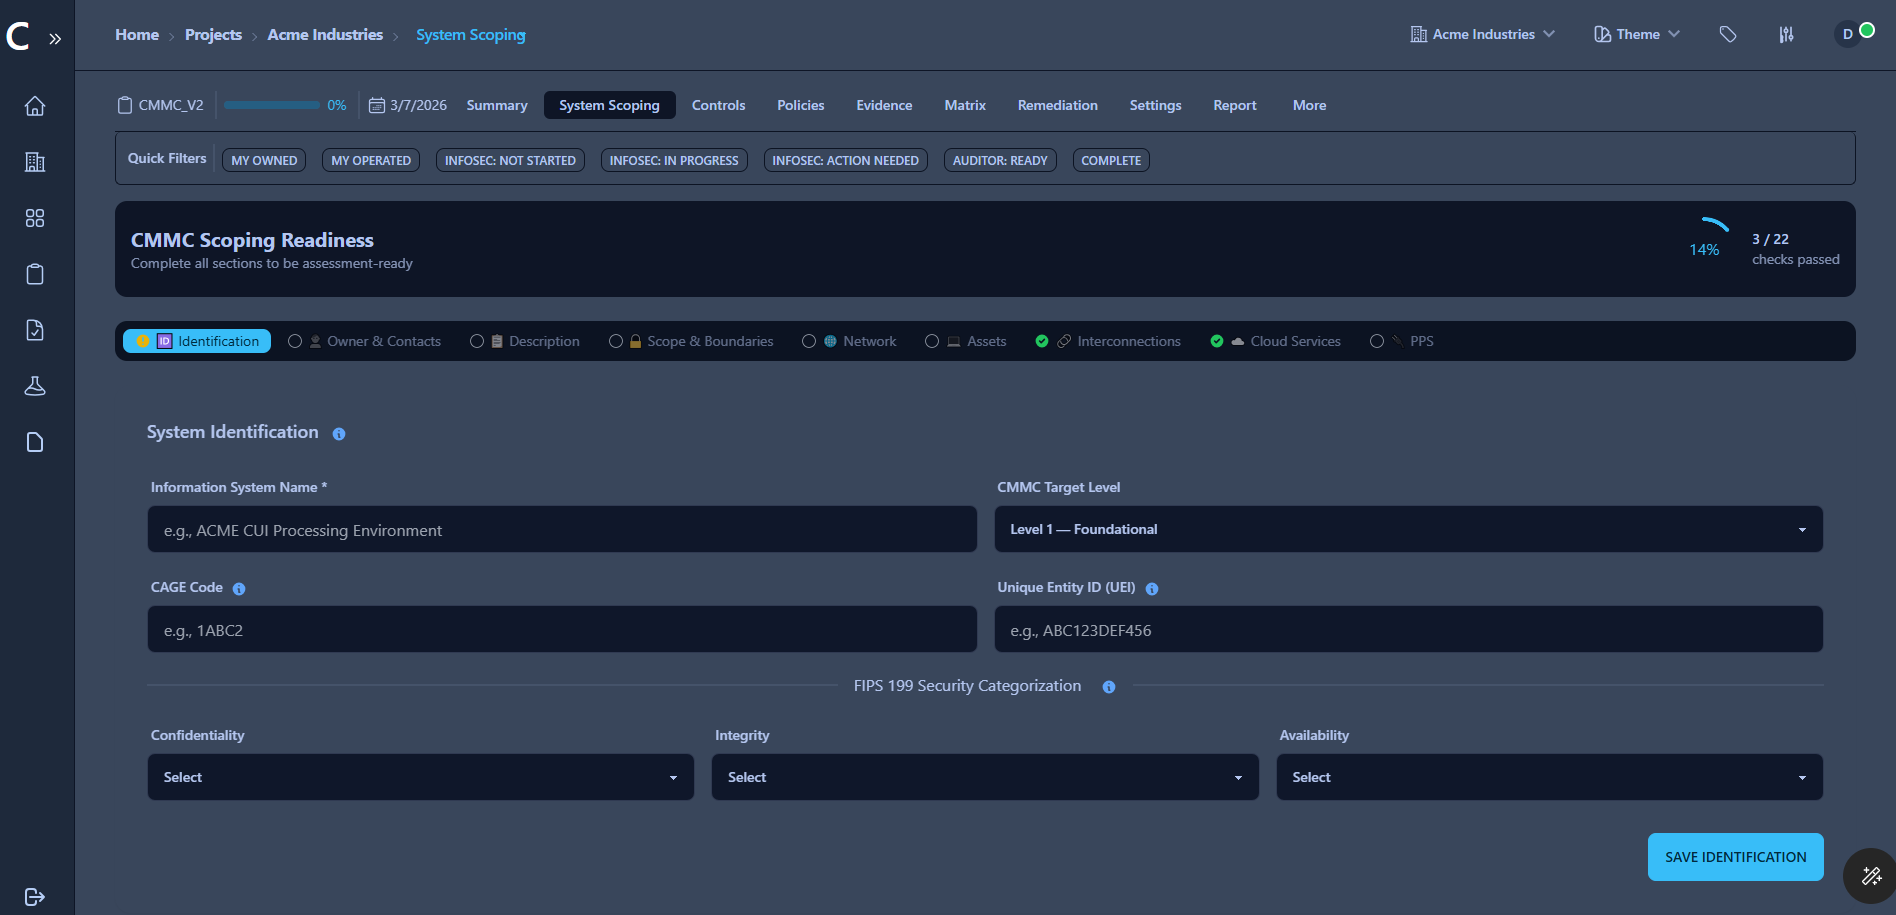
What it covers
Asset Management in CyberComply
Asset records
Capture the systems, services, and environments relevant to the program.
Categorization
Group assets in the way your framework and organization describe them.
Boundary clarity
Make the in-scope environment explicit so scoping decisions can be reviewed.
Ownership
Know who is responsible for each system.
Related capabilities
Connected parts of the platform
Related frameworks
Where this capability applies
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.