
Capability
One organized requirement library behind every framework.
Organize the requirements, practices, and controls that apply to your organization, with ownership and implementation detail attached to each.
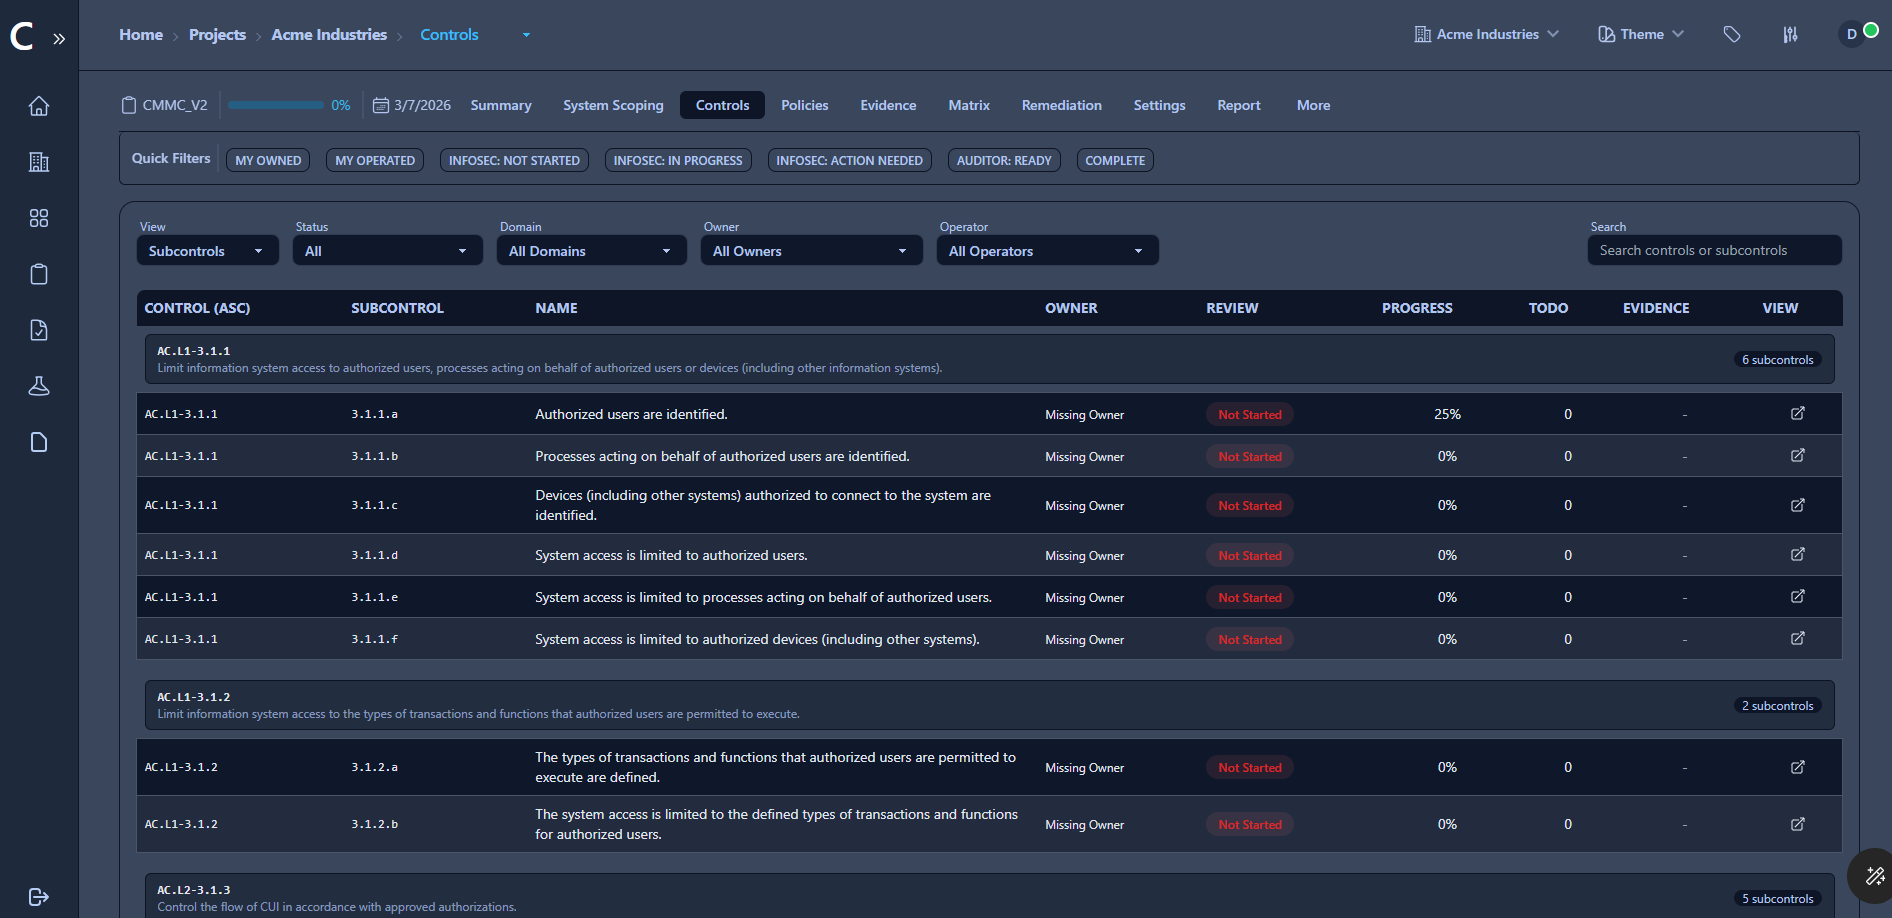
Compliance frameworks express expectations as requirements, practices, or controls. CyberComply organizes them in one structured library so teams work from the same definitions.
Each requirement carries the context a reviewer asks for: who owns it, how it is implemented in this environment, what supports that claim, and what remains open.
What it covers
Controls & Requirements in CyberComply
Requirement library
Framework requirements organized by family, domain, or control group.
Ownership
Assign a responsible owner so accountability is explicit rather than assumed.
Implementation detail
Describe how the requirement is satisfied in your environment, in your own words.
Linked evidence
Associate the artifacts that support the described implementation.
Status visibility
See where each requirement stands and which ones still need attention.
Related capabilities
Connected parts of the platform
Related frameworks
Where this capability applies
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.