
Federal & Defense
NIST SP 800-171
Protecting CUI in nonfederal systems.
NIST SP 800-171 defines security requirements for protecting Controlled Unclassified Information in nonfederal systems and organizations. It is referenced widely across federal contracting and underpins CMMC Level 2 expectations.
The requirements are organized into families covering areas such as access control, audit and accountability, configuration management, incident response, and system protection. Each requirement decomposes into assessment objectives.
Who it applies to
- Contractors and subcontractors that process, store, or transmit CUI
- Organizations subject to DFARS clauses referencing 800-171
- Suppliers receiving flow-down CUI requirements
- Organizations preparing for a CMMC Level 2 assessment
Reporting and visibility
- Requirement family coverage
- Objective status
- Evidence gaps
- Open POA&M items
- Remediation progress
Challenges
What makes this framework hard to manage
Objective-level detail
Teams track requirements at a summary level and miss the objectives underneath.
Implementation statements
Describing how each requirement is met in this environment is the slowest part of the work.
Evidence traceability
Reviewers ask which artifact supports which requirement, and the answer is often verbal.
Scoring maintenance
Self-assessment scores go stale as the environment changes.
How CyberComply helps
Supporting NIST 800-171 work
Requirement families
Work through the requirement set in an organized structure rather than a flat spreadsheet.
Objective evaluation
Record status at the objective level so partial implementation is visible.
Implementation detail
Capture how each requirement is satisfied in your environment.
Evidence association
Attach the artifacts that substantiate each requirement.
SSP and POA&M
Organize the plan information and track deficiencies to closure.
Workflow
A structured path for this framework
- Scope
- Assess
- Identify Gaps
- Remediate
- Document
- Prepare
- Maintain
Modules
Capabilities most used for this framework
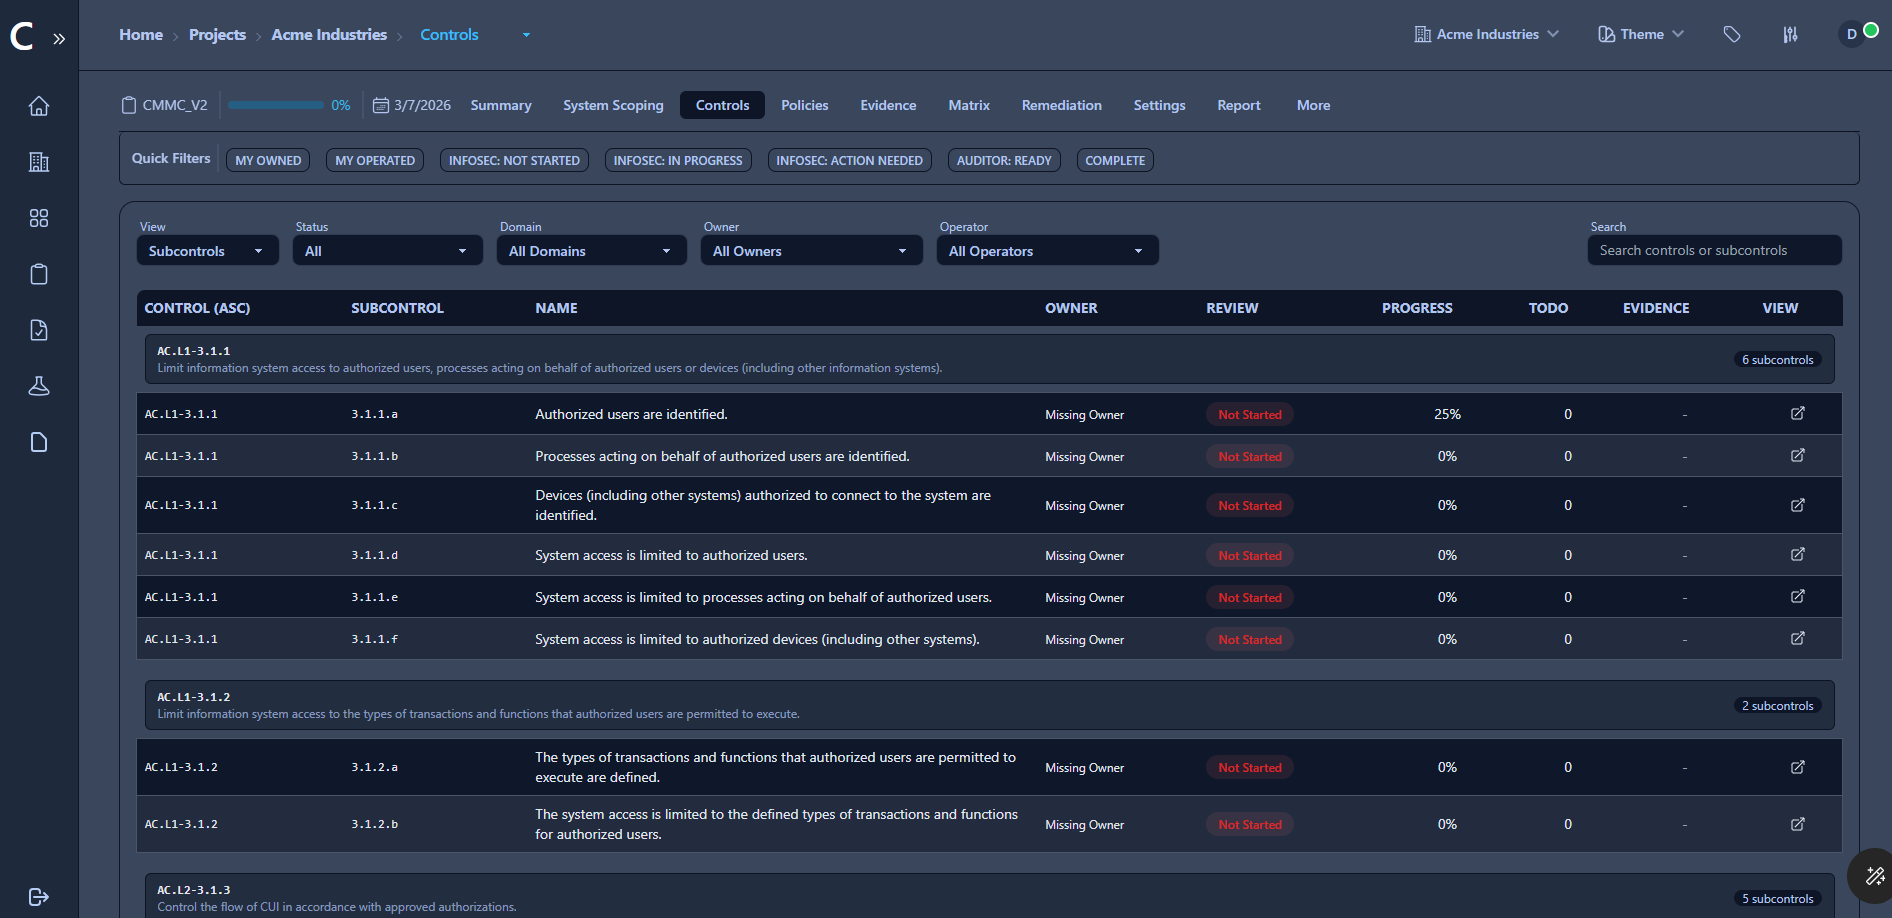
Controls & Requirements
Organize the requirements, practices, and controls that apply to your organization, with ownership and implementation detail attached to each.
Read more →Assessments
Evaluate requirements and assessment objectives using consistent statuses so progress is measurable rather than anecdotal.
Read more →Evidence Management
Keep supporting documentation associated with the requirements it proves, with ownership, review status, and dates that hold up under review.
Read more →SSP & POA&M
Structure the information needed to develop and maintain a System Security Plan, and track deficiencies through a Plan of Action & Milestones.
Read more →Remediation
Move from identifying a deficiency to resolving it with priorities, owners, tasks, due dates, and evidence of closure.
Read more →FAQ
NIST 800-171 questions
How does 800-171 relate to CMMC?
CMMC Level 2 aligns with the security requirements in NIST SP 800-171. Work performed against 800-171 is directly relevant, but each program keeps its own status and accountability.
Does CyberComply calculate our score for us?
CyberComply maintains the requirement status information your team uses. Determining and reporting a score remains your organization's responsibility.
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Related frameworks
Often managed alongside this one
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.