
Commercial & Regulatory
SOC 2
Trust services criteria for service organizations.
SOC 2 reports address the trust services criteria relevant to a service organization — commonly security, and optionally availability, processing integrity, confidentiality, and privacy. Reports are issued by a licensed CPA firm following an examination.
Evidence expectations, particularly for Type 2 reports covering a period of time, are where most organizations struggle.
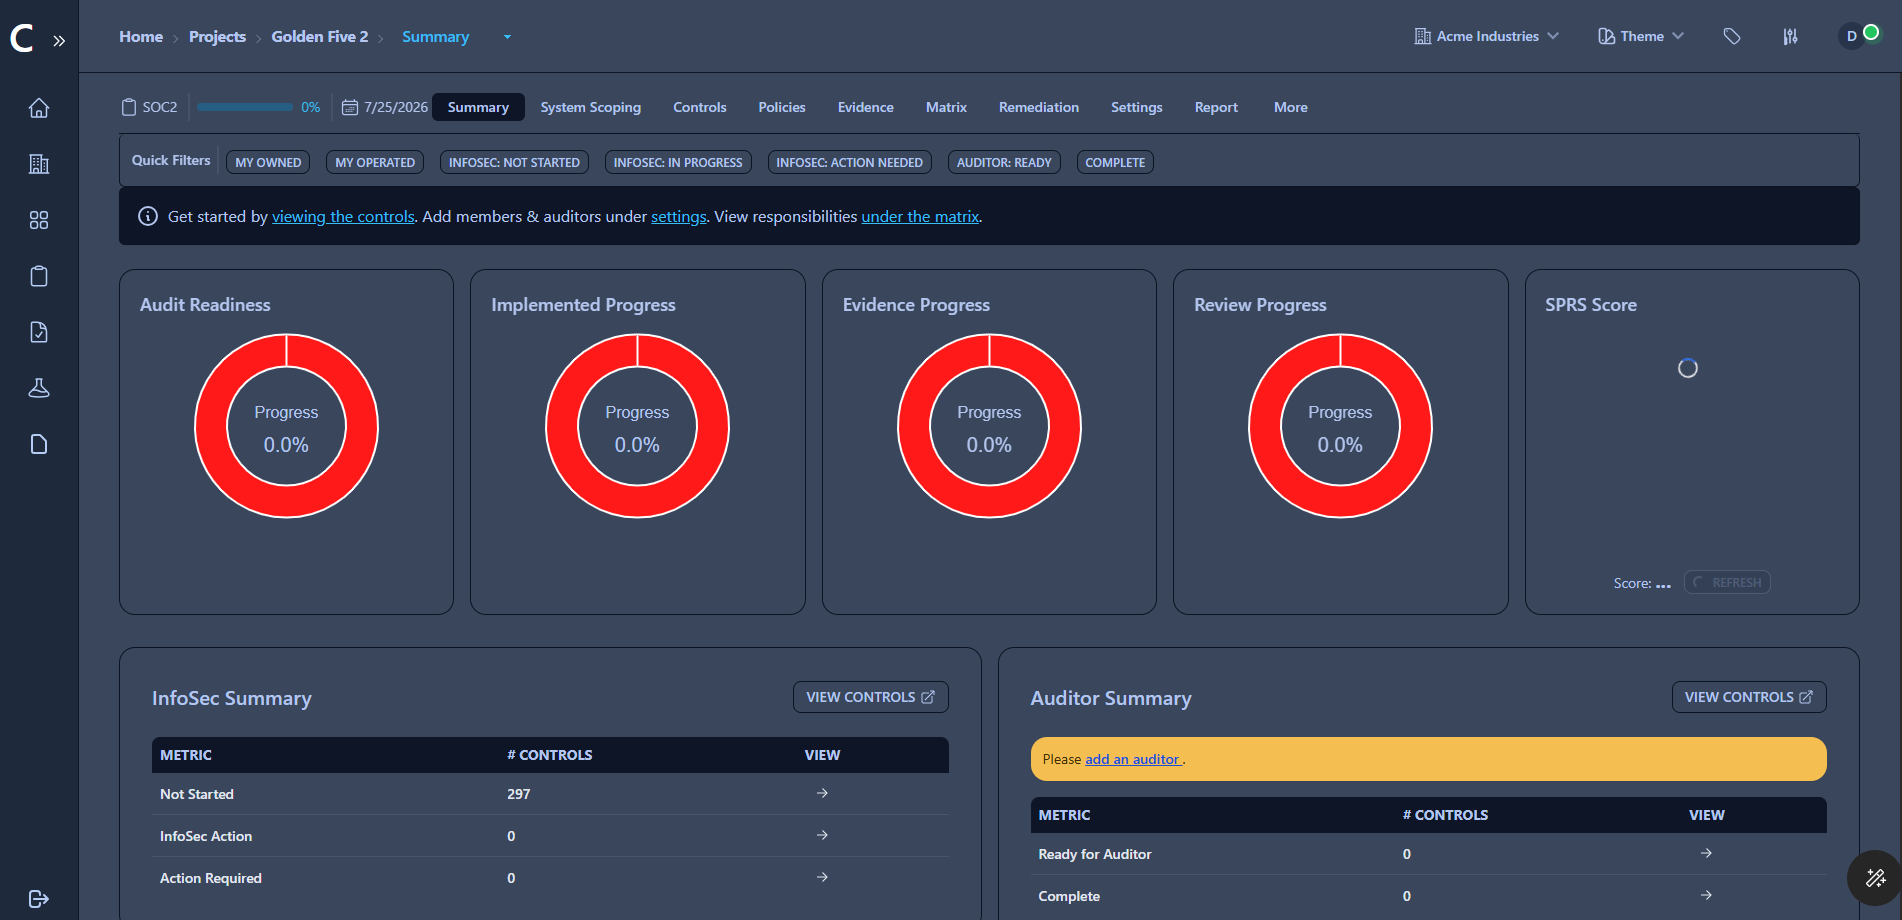
Who it applies to
- SaaS and technology service providers
- Service organizations whose customers require a report
- Companies entering enterprise sales cycles
- Organizations maintaining an existing report annually
Reporting and visibility
- Criteria coverage
- Evidence status
- Open findings
- Remediation progress
Challenges
What makes this framework hard to manage
Period-of-time evidence
A Type 2 examination looks across a window, not at a single day.
Control description drift
Descriptions written at the start of the period stop matching practice.
Request list chaos
Auditor requests arrive by email and are answered from scattered sources.
How CyberComply helps
Supporting SOC 2 work
Criteria organization
Structure the applicable criteria with owners and control descriptions.
Evidence discipline
Keep supporting material attached to the criteria it addresses, with dates and review state.
Remediation
Close gaps found in readiness work before the examination period.
Status visibility
Know what is still outstanding without a spreadsheet reconciliation.
Workflow
A structured path for this framework
- Scope
- Assess
- Identify Gaps
- Remediate
- Document
- Prepare
- Maintain
Modules
Capabilities most used for this framework
Controls & Requirements
Organize the requirements, practices, and controls that apply to your organization, with ownership and implementation detail attached to each.
Read more →Evidence Management
Keep supporting documentation associated with the requirements it proves, with ownership, review status, and dates that hold up under review.
Read more →Remediation
Move from identifying a deficiency to resolving it with priorities, owners, tasks, due dates, and evidence of closure.
Read more →Tasks & Workflow
Assign, prioritize, and track the work that moves the program forward, connected to the requirements it relates to.
Read more →Reporting & Dashboards
See compliance posture, framework progress, open findings, remediation status, evidence state, and overdue work in one view.
Read more →FAQ
SOC 2 questions
Does CyberComply produce a SOC 2 report?
No. A SOC 2 report is issued by a licensed CPA firm following an examination. CyberComply supports readiness and ongoing management of the underlying program.
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Related frameworks
Often managed alongside this one
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.