
Governance · Risk · Compliance
One GRC platform. Multiple frameworks. One source of truth.
CyberComply brings requirements, assessments, evidence, risks, policies, remediation, documentation, and assessment readiness into a single environment — so your compliance program stops living in spreadsheets and shared drives.
Built by Armada Cyber Defense LLC for organizations managing real compliance obligations.
The problem
Compliance work is scattered across too many places
Most organizations track requirements in one place, evidence in another, risks in a third, and remediation in email. Nothing reconciles, and assessment preparation becomes a scramble.
Spreadsheet sprawl
Requirement trackers drift out of date and no one is certain which version is current.
Evidence scattered
Screenshots, policies, and exports live in shared drives with no link to the requirement they satisfy.
Duplicated effort
Overlapping frameworks are worked separately, so the same control is assessed several times.
Assessment scramble
Preparation starts late because the current state of the program is never visible in one place.
The platform
See your compliance program clearly
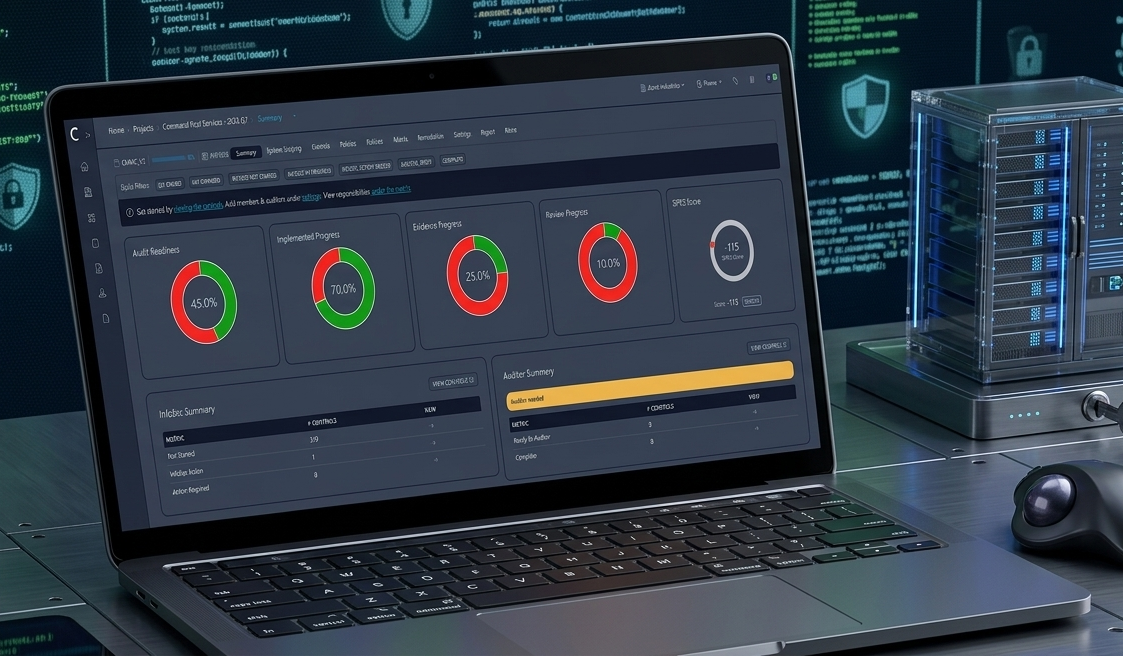
Centralize assessments, requirements, controls, evidence, risks, remediation, documentation, and compliance progress in one environment.
Single environment
CyberComply GRC
- 01Frameworks
- 02Controls
- 03Assessments
- 04Evidence
- 05Policies
- 06Risks
- 07Assets
- 08Vendors
- 09Remediation
- 10SSP / POA&M
- 11Tasks
- 12Reporting
Interconnected components of the same environment — not separate tools stitched together.
Capabilities
What you can manage in CyberComply
Each capability is a component of the same environment, sharing requirements, evidence, ownership, and status.
Assessments
Evaluate requirements and assessment objectives using consistent statuses so progress is measurable rather than anecdotal.
Read more →Controls & Requirements
Organize the requirements, practices, and controls that apply to your organization, with ownership and implementation detail attached to each.
Read more →Evidence Management
Keep supporting documentation associated with the requirements it proves, with ownership, review status, and dates that hold up under review.
Read more →Risk Management
Maintain a risk register with ownership, likelihood, impact, scoring, mitigation, and review dates alongside your compliance program.
Read more →Policies & Procedures
Maintain a policy inventory with ownership, versioning, review cycles, and the controls each document supports.
Read more →SSP & POA&M
Structure the information needed to develop and maintain a System Security Plan, and track deficiencies through a Plan of Action & Milestones.
Read more →Remediation
Move from identifying a deficiency to resolving it with priorities, owners, tasks, due dates, and evidence of closure.
Read more →Asset Management
Maintain the systems, environments, and asset records that define the boundary your compliance program applies to.
Read more →Frameworks
Supported compliance frameworks
Work multiple frameworks in one environment and organize overlapping requirements instead of repeating them.
Federal & Defense
CMMC
DoD contractors handling FCI and CUI.
Federal & Defense
NIST SP 800-171
Protecting CUI in nonfederal systems.
Federal & Defense
NIST Cybersecurity Framework
Organizing cybersecurity risk outcomes.
Federal & Defense
NIST SP 800-53
Security and privacy controls for information systems.
Commercial & Regulatory
ISO 27001
Information security management systems.
Commercial & Regulatory
SOC 2
Trust services criteria for service organizations.
Commercial & Regulatory
HIPAA
Safeguards for protected health information.
Commercial & Regulatory
PCI DSS
Protecting cardholder data environments.
How it works
A repeatable compliance workflow
The same structured path applies whether you are starting your first framework or maintaining several.
- 01
Scope
Determine applicable environments, systems, organizations, and requirements.
- 02
Assess
Evaluate current implementation against applicable requirements and objectives.
- 03
Identify Gaps
Identify missing, incomplete, or insufficient controls and evidence.
- 04
Remediate
Assign ownership, priorities, dates, tasks, and corrective actions.
- 05
Document
Maintain policies, evidence, SSP information, POA&Ms, risks, and supporting records.
- 06
Prepare
Organize the environment for internal review, customer review, audit, or assessment.
- 07
Maintain
Continue monitoring progress and maintaining the program after the initial assessment.
Who it's for
Built for the organizations doing the compliance work
From a single small business preparing for its first assessment to consultants managing many client environments.
Defense Contractors
CMMC, CUI readiness, SSP, POA&M, and assessment preparation.
Read more →Federal Contractors
Contractual, regulatory, and customer-driven requirements in one place.
Read more →Small & Mid-Sized Businesses
Structured GRC without enterprise complexity.
Read more →Consultants
Standardized methodology across every client engagement.
Read more →MSPs / MSSPs
Deliver compliance services across multiple customer tenants.
Read more →Enterprises
Multiple frameworks, business units, vendors, and governance obligations.
Read more →Multi-Entity Organizations
Centralized visibility with controlled access across entities.
Read more →CyberGap
Not sure where to start?
Start with a free CMMC gap assessment. CyberGap helps you identify gaps, understand your current posture, and determine where attention is needed before implementing a broader compliance-management program. No sales form required.
FAQ
Common questions
What is CyberComply?
CyberComply is a governance, risk, and compliance software platform. It gives an organization one environment for compliance frameworks, requirements, controls, assessments, evidence, policies, risks, remediation, documentation, and reporting. It is a product of Armada Cyber Defense LLC.
Is CyberComply only for CMMC?
No. CyberComply is a multi-framework GRC platform. It has particularly strong capabilities for organizations in the U.S. federal and Defense Industrial Base ecosystem, but the same environment supports other frameworks including NIST SP 800-171, NIST CSF, NIST SP 800-53, ISO 27001, SOC 2, HIPAA, and PCI DSS.
Does CyberComply certify my organization?
No. CyberComply is software that supports readiness and compliance management. It does not issue certifications, and using it does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Does CyberComply replace a C3PAO?
No. Formal CMMC assessment and certification are performed by authorized third-party assessment organizations. That is a separate activity from the software-supported readiness and compliance management CyberComply provides.
Can CyberComply support multiple frameworks?
Yes. Organizations can manage several frameworks in the same environment. CyberComply helps identify related requirements and reuse applicable evidence, while each framework retains its own status and accountability. Satisfying a requirement in one framework does not make an organization compliant with another.
Can evidence be associated with multiple requirements?
Yes. Where the same artifact validly supports more than one requirement, it can be associated with each of them rather than duplicated. The association is a decision your team makes and records.
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.