
Capability
Do the work once. Apply it across your compliance environment.
Identify related requirements across frameworks and reuse applicable evidence, while keeping framework-specific accountability intact.
Many frameworks express related security and governance concepts in different language. Organizations that manage each framework in isolation redo work that was already done.
CyberComply helps organize requirements and supporting evidence so related items can be identified and applicable evidence reused where the mapping is valid.
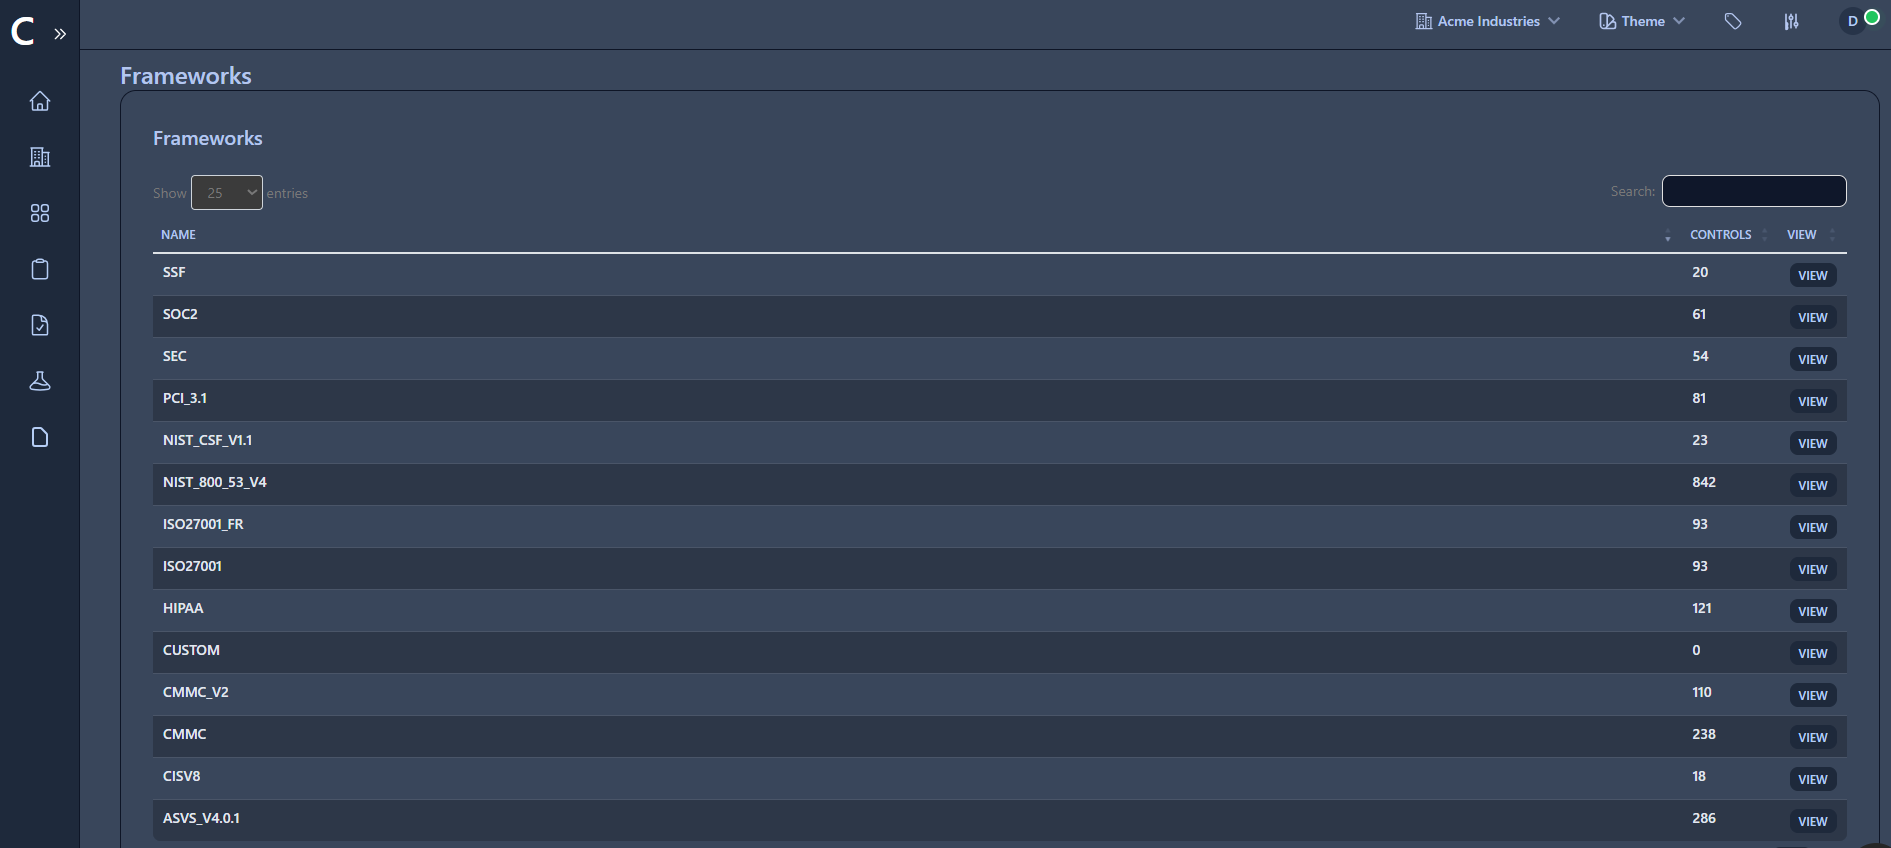
What it covers
Cross-Framework Mapping in CyberComply
Identify related requirements
Surface requirements across frameworks that address related concepts.
Understand framework overlap
See where programs converge and where they genuinely differ.
Reuse applicable evidence
Associate an artifact with each requirement it validly supports.
Reduce duplicate compliance work
Avoid rebuilding a program from scratch for each new framework.
Maintain framework-specific accountability
Satisfying a requirement in one framework does not make an organization compliant with another. Each framework keeps its own status and its own record.
Related capabilities
Connected parts of the platform
Related frameworks
Where this capability applies
CyberComply is a software platform that assists organizations in managing governance, risk, compliance, documentation, and readiness activities. Using CyberComply does not by itself guarantee regulatory compliance, certification, authorization, or a successful assessment.
Ready to bring your compliance program together?
See how CyberComply can help centralize requirements, evidence, risks, remediation, documentation, and assessment readiness.